Product Security
Our Approach to Product Security
As a provider of industrial equipment and control systems, SINFONIA TECHNOLOGY CO., LTD. (hereinafter “SINFONIA”) recognizes that cybersecurity risks inherent in products may affect product safety, reliability, and business continuity.
To help customers use our products and services with confidence, we work to ensure security throughout the product lifecycle, from planning and design through development, manufacturing, operation after shipment, and disposal.
Risk-Based Security Measures
We identify and assess cybersecurity risks by considering the intended use of each product, its anticipated operating environment, connectivity, and potential threats. Based on this assessment, we implement reasonable and appropriate security measures.
Security Throughout the Product Lifecycle
We consider product security throughout the entire product lifecycle:
Planning → Design → Development → Verification → Manufacturing → Inspection and Testing → Shipment → Operation → Disposal
Secure by Design
We treat security as an integral part of product development rather than as an add-on. Security considerations are incorporated into product design and development from the earliest stages.
Product Vulnerability Management
We continuously monitor vulnerability information relevant to our products. When a vulnerability is identified, we assess its potential impact, implement appropriate corrective or mitigating measures, and provide relevant information to customers as necessary.
Governance and Responsibilities
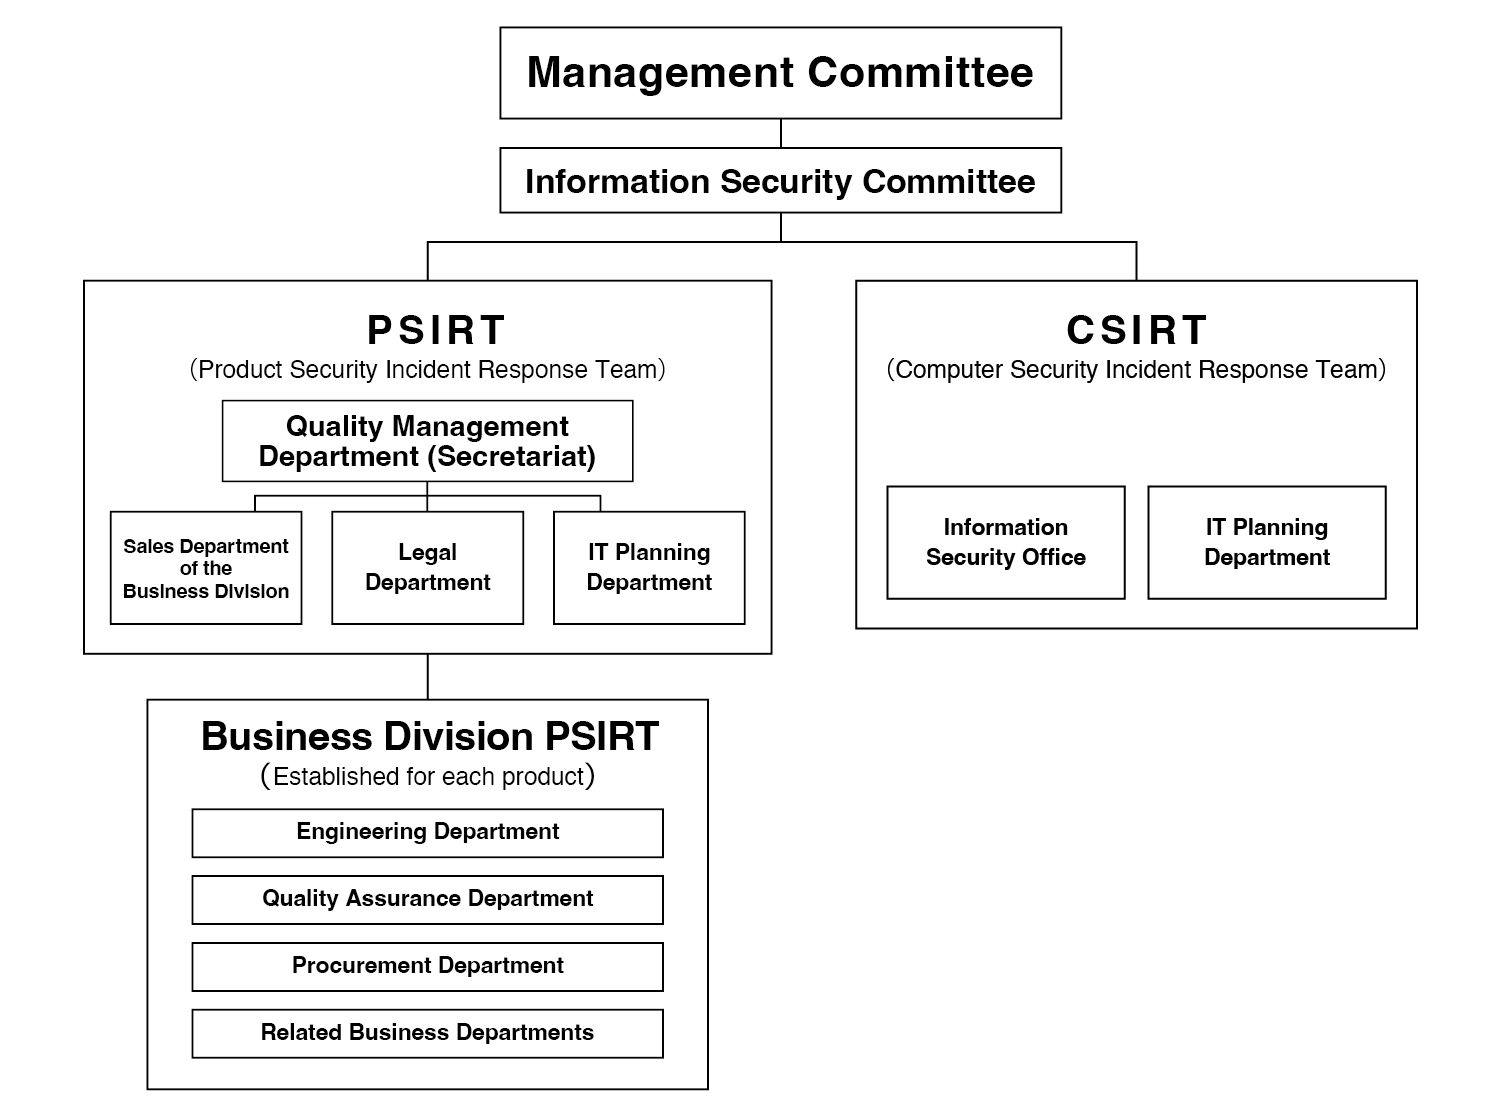
We clearly define roles and responsibilities for product security and address product security matters in a planned and coordinated manner through our Product Security Incident Response Team (PSIRT) and Computer Security Incident Response Team (CSIRT).
Compliance
Our officers, employees, and contractors comply with this policy and all related internal rules and procedures and work to maintain product security.
Response to Product Security Issues
If a product security issue arises from a vulnerability or other security weakness in a SINFONIA product, we promptly take appropriate measures to contain the impact and address the issue.
Continuous Improvement
We continuously review and improve this policy and our product security activities in response to changes in the threat landscape, technological developments, applicable laws and regulations, and customer requirements. We also provide ongoing education and awareness activities to strengthen product security awareness across our organization.
Product Security Organization
SINFONIA has established a Product Security Incident Response Team (PSIRT) to address vulnerabilities and security issues involving our products and services.
The Quality Management Department serves as the PSIRT secretariat. The PSIRT works with relevant functions, including business divisions,legal, and IT. Within each business division, engineering, quality assurance, procurement, and other functions associated with the affected product investigate potential impact and consider appropriate measures.
The PSIRT also shares information and coordinates response activities with SINFONIA’s internal Computer Security Incident Response Team (CSIRT).
Vulnerability Disclosure Policy
SINFONIA works with security researchers, customers, business partners, and other relevant parties to address vulnerabilities affecting our products and services, with the aim of preventing security incidents and minimizing potential impact.
Coordinated Vulnerability Disclosure
We coordinate with individuals and organizations that discover or report vulnerabilities. As a general rule, SINFONIA does not publicly disclose information about an unremediated vulnerability until a fix, mitigation, or workaround is available.
Protection for Good-Faith Reporting
SINFONIA will not subject a person who reports a vulnerability in good faith to adverse treatment, legal action, or retaliation in connection with the report.
Compliance with Legal and Contractual Requirements
We disclose vulnerability information at an appropriate time and in an appropriate manner, in accordance with applicable laws and regulations, including the EU Cyber Resilience Act where applicable, and our contractual obligations to customers.
Publication of Vulnerability Information
If we determine that a vulnerability may affect customers or other relevant parties, we publish information through our “Security Advisories”, together with available corrective measures, mitigations, or workarounds, as appropriate.
Report a Product Security Vulnerability
SINFONIA accepts reports of potential security vulnerabilities affecting our products and services. If you believe you have identified a security issue, please submit a report using the form below.